Code reviews,
without the bottleneck.
Revyn reviews every pull request automatically. Catch bugs, security issues, and risky changes before they reach production.
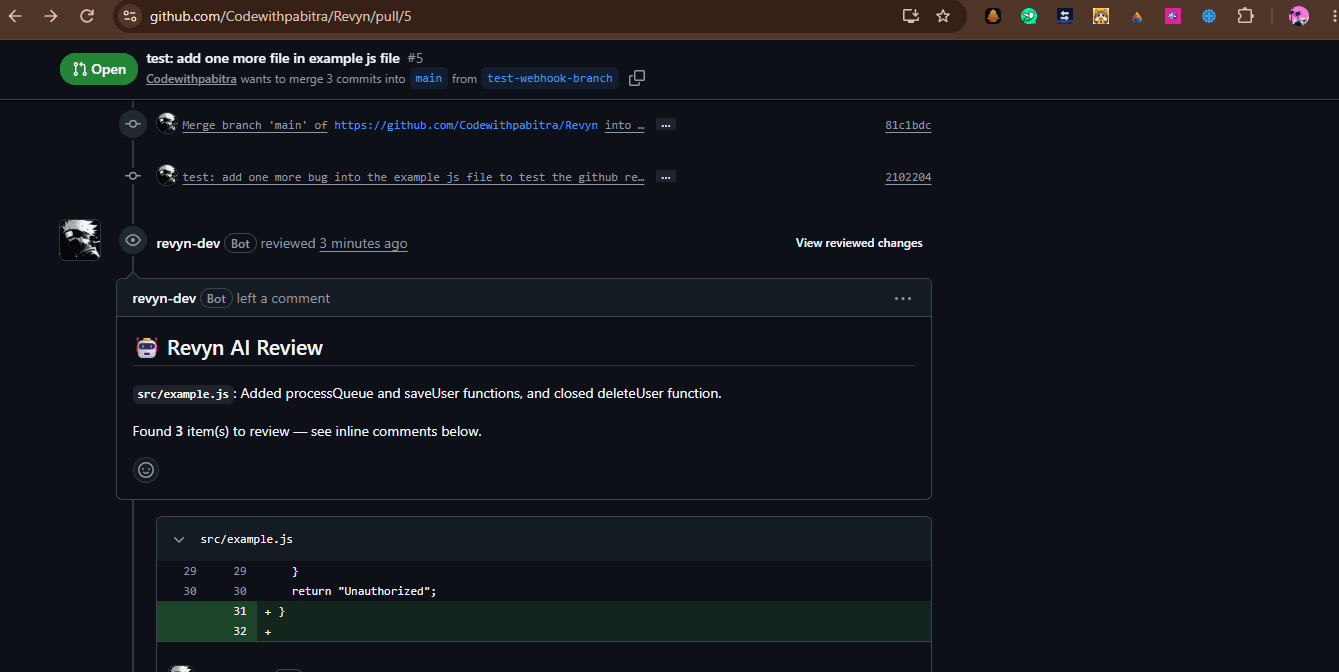
Comments where they matter
Actionable feedback, right beside the lines that need attention.
Catch bugs before merge
Surface logic errors, risky changes, and potential security issues.
Fits your GitHub workflow
Review pull requests without adding another step to your process.
From first commit
to a sharper review.
Your existing GitHub workflow, with another set of eyes on every change.
Open a pull request
Push your changes and open a PR like you always do. Revyn works through your GitHub integration.
Inspect the changes
Revyn analyzes the diff for potential logic errors, risky changes, and security issues.
Review the findings
Read actionable comments directly in your pull request and decide what needs fixing before merge.
Not every diff
deserves a comment.
Code reviews should help you ship with confidence, not bury you in noise. Revyn focuses on potential bugs, security issues, and risky logic worth investigating.
Relevant findings. Less noise.
Security
Potential vulnerabilities
Logic
Bugs and edge cases
Sensitive changes
Risky code paths
PR context
Changes in context
Your codebase deserves
another pair of eyes.
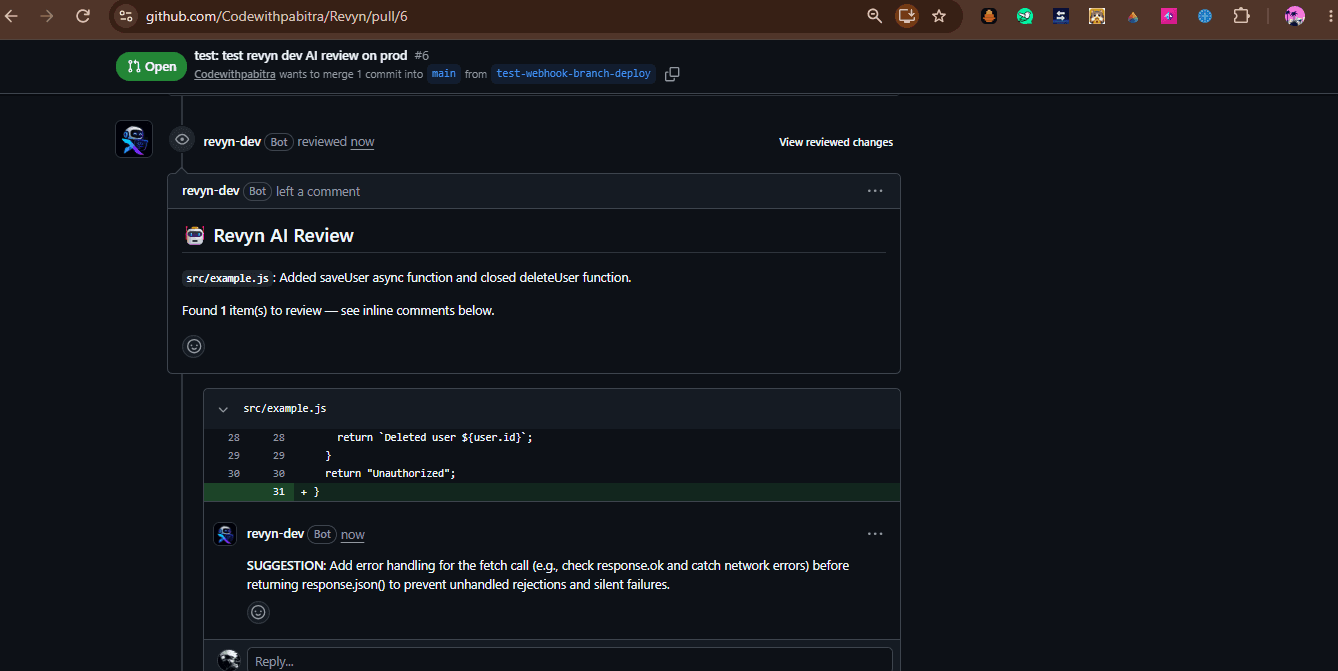
Average time to first review comment.
Less irrelevant noise.
Keep reviews focused on meaningful changes.
No extra place to check.
Review comments live alongside your pull request, keeping your existing workflow intact.
A second look at
every important change.
Explore an illustrative review to see how potential issues can be surfaced alongside the code that needs attention.
feat: improve authentication
example-project / pull request #42
Example code only. Whether authorization is required depends on the application's access-control rules.
Review findings
Illustrative output
The review starts here.
Reveal the sample findings to explore the kind of feedback a code review might surface.
Interactive demo · No repository is analyzed
Thoughtful by design
Your workflow.
With another pair of eyes.
Your pull request
Review where you already work.
Bring automated analysis into your existing GitHub workflow without making another dashboard the center of your day.
Security-aware reviews
Surface potentially risky patterns before changes reach production.
Find meaningful bugs
Focus attention on logic errors and behavior that deserves a second look.
Where the code lives
Keep review feedback close to the changed lines in your pull request.
FAQ
Got questions? We've got answers.
Everything you need to know before bringing Revyn into your workflow.
Revyn is an AI-powered code reviewer that analyzes GitHub pull requests to help identify potential bugs, security risks, and logic issues before your code gets merged.
Ship faster.
Review smarter.
Connect your GitHub repository and let Revyn handle the first pass on every pull request.
Connect GitHub